Crafty Falcon is an AI-assisted hacking campaign that CERT-In says is stealing money from Indian fintechs, NBFCs and payment firms through their own payment APIs. Here’s how it works and what it means for you
India’s cybersecurity agency has given a name to the AI-powered attackers hitting the financial sector. On November 4, 2026, CERT-In issued a Critical advisory naming the threat actor Crafty Falcon, a group that uses publicly available AI hacking tools to find weaknesses, plan attacks and move money at “machine speed”. The targets include NBFCs, digital lenders, fintech companies, payment aggregators and crypto exchanges. CERT-In says the threat is active and ongoing, and some companies have been hit again even after fixing earlier problems. Here’s what we know so far.
Quick Answer
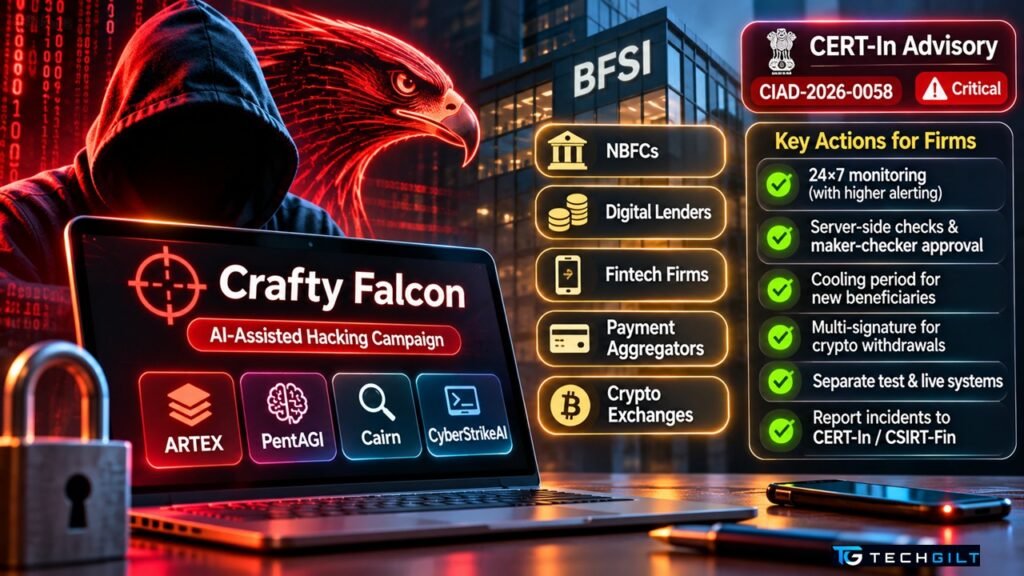
Crafty Falcon is the name CERT-In’s financial-sector team, CSIRT-Fin, has given to an AI-assisted threat actor attacking India’s BFSI sector. Advisory CIAD-2026-0058 (4 November 2026, rated Critical) says the group uses four publicly available AI offensive-security tools, ARTEX, PentAGI, Cairn and CyberStrikeAI, to find weaknesses and then call the victim’s own payment and disbursement APIs to transfer money. The stolen funds are moved over IMPS and NEFT to mule accounts at several banks. CERT-In has asked BFSI entities to treat the campaign as an “immediate and continuing threat”.
What CERT-In Said About Crafty Falcon
The new advisory, CIAD-2026-0058, is an update to an earlier advisory from 9 October 2026 (CIAD-2026-0046) about attackers misusing payment and disbursement APIs. TechGilt covered that first warning in CERT-In Warns of API Attacks.
According to CERT-In, continued analysis of reported incidents showed a significant escalation. CSIRT-Fin describes the group as a financial threat actor that “surveys its targets with machine intelligence, operates at machine speed” and strikes by using the victim’s own payment systems.
Two details stand out:
- Repeat attacks: some organisations that had already received the earlier warnings and fixed their systems were attacked again.
- New targets: crypto exchanges and virtual digital asset providers are now named, alongside lenders and payment firms.
How the Crafty Falcon Attacks Work
Based on CERT-In’s advisories and reporting by BW Businessworld, a typical attack follows these stages:
- Find a way in: AI tools scan for weak spots in internet-facing systems, cloud setups and unpatched software.
- Plan with AI: the tools generate custom attack scripts and can run a whole sequence of steps on their own.
- Use the company’s own APIs: instead of hacking customer accounts, the attackers call the company’s payment, payout or merchant settlement APIs to send money out.
- Move the money fast: funds go over IMPS and NEFT to mule accounts spread across several banks and are withdrawn quickly.
- Cover the tracks: attackers delete logs and tamper with security software to slow down investigators.
This is why CERT-In calls it machine speed: what once took a skilled team days can now be automated in hours.
The 4 AI Tools Behind Crafty Falcon
| Tool | What it is |
|---|---|
| ARTEX | Open-source, multi-agent AI penetration-testing and command-and-control platform |
| PentAGI | Autonomous multi-agent AI penetration-testing system |
| Cairn | AI-powered attack search engine |
| CyberStrikeAI | AI framework for offensive security testing |
These tools were built for security testing, to help companies find their own weaknesses. The attackers are using them for the opposite purpose. It’s a clear example of how agentic AI (AI that can carry out multi-step tasks on its own) can be turned against the very systems it was meant to protect.
Who Is Being Targeted
CERT-In’s list of affected entities includes:
- NBFCs (non-banking financial companies)
- Digital lending platforms
- Fintech companies
- Payment aggregators and payment service providers
- Crypto exchanges and virtual digital asset service providers
CERT-In has not identified the people behind the campaign and has not said whether the campaign is state-sponsored.
What CERT-In Wants Financial Firms to Do
The advisory gives detailed guidance. The key points:
- 24×7 monitoring, with more staff and lower alert thresholds on weekends and holidays, when attackers expect slower responses.
- Server-side checks on every payment and settlement request, plus maker-checker approval (a second person approves) for payment aggregators.
- Cooling periods for new beneficiaries and limits on how fast and how often money can be sent, for digital lenders.
- Multi-signature approval for crypto withdrawals.
- Separate test and live systems, and watch for AI hacking tools or unusual AI API traffic on servers that shouldn’t use them.
- Report incidents with logs to CERT-In/CSIRT-Fin at incident@cert-in.org.in.
What Crafty Falcon Means for Ordinary Customers
The attacks target the companies’ own payment systems, not individual customers’ phones or passwords. Neither CERT-In advisory says whether customer accounts were affected. Still, it’s a good time for basic care:
- Check your statements from lending apps, wallets and payment apps for anything unusual.
- Use well-known, RBI-regulated lenders and apps, not unknown loan apps.
- Never share OTPs or PINs, even if a caller claims to be from your bank or “CERT-In”.
- Report fraud quickly: call 1930 or file a complaint at cybercrime.gov.in.
What We Don’t Know Yet
- How much money has been stolen in total.
- Which companies have been hit. CERT-In has not named them.
- Who is behind the attacks, and where they operate from.
CERT-In Warns of API Attacks
AI Fraud Detection in Banks
Frequently Asked Questions
What is Crafty Falcon?
Crafty Falcon is the name CERT-In has given to an AI-assisted threat actor attacking India’s financial sector. It uses public AI hacking tools to break in and then misuses companies’ own payment APIs to transfer money.
Which AI tools does Crafty Falcon use?
CERT-In names four publicly available tools: ARTEX, PentAGI, Cairn and CyberStrikeAI. All four were designed for security testing.
Is my bank account at risk from Crafty Falcon?
The attacks target the payment systems of fintechs, lenders and payment firms, not individual customers. CERT-In has not said that customer accounts were affected, but you should still check statements and never share OTPs.
Which companies were attacked?
CERT-In has not named any companies. It lists the types of targets: NBFCs, digital lenders, fintechs, payment aggregators, payment service providers and crypto exchanges.
How do I report cyber fraud in India?
Call the national cybercrime helpline 1930 or file a complaint at cybercrime.gov.in. Companies should report incidents to CERT-In at incident@cert-in.org.in.
Conclusion
Crafty Falcon shows how quickly AI has changed cybercrime. Tools built to test security are now being used to find weaknesses, automate attacks and move money through a company’s own payment systems in hours. CERT-In’s Critical rating, the repeat attacks on firms that had already made fixes, and the addition of crypto exchanges all point to a campaign that is growing. For fintechs and lenders, the message is to monitor round the clock and lock down payment APIs. For customers, the best defence is still watching your statements and reporting fraud quickly.
My take: I believe Crafty Falcon sheds light on how artificial intelligence is transforming the cybersecurity landscape. Attackers have moved beyond relying solely on traditional hacking methods; instead, they are leveraging AI to identify vulnerabilities, automate attacks and exploit legitimate payment systems. This creates further challenges for banks, fintech firms and digital lending platforms.
Organisations should strengthen API security, implement continuous monitoring and adopt robust authentication controls. For professionals and students in the cybersecurity field, this incident serves as a reminder of the evolving nature of cyber threats and the necessity for continuous education and training. I would like to conclude by saying: “When AI makes cyberattacks faster, our defence must become smarter, stronger and more proactive.”
Over to You
Do you think Indian fintechs are ready for AI-powered attacks like Crafty Falcon? Share your thoughts in the comments below.