Hackers are using stolen API keys to move money out of Indian fintechs and lenders without any OTP. Here’s what happened, how the attacks work, and what it means for you
India’s national cybersecurity agency has raised a critical alarm for the country’s digital lending and payments industry. In a new CERT-In advisory, the agency warns that hackers are breaking into fintech systems, stealing the “keys” that connect them to banks, and quietly sending money to their own accounts, all without a single OTP, fake call or customer mistake. Media reports say about 20 financial institutions were hit earlier this month. Here’s what the CERT-In advisory says, how these attacks work, and what you should do as a customer.
Quick Answer
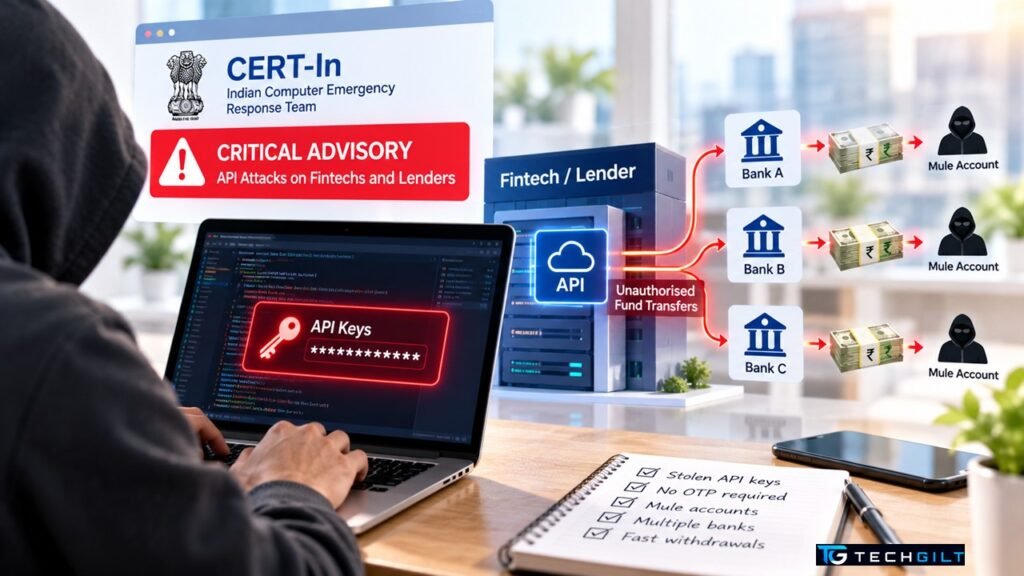
On October 9, 2026, CERT-In (the Indian Computer Emergency Response Team) and its finance-sector unit CSIRT-Fin issued a critical advisory (CIAD-2026-0046) warning NBFCs, digital lenders, fintech firms, payment companies and wallet operators about attacks on their payment and loan-disbursement APIs. Attackers steal API credentials, then send money directly from the company’s own trusted servers, bypassing KYC, beneficiary checks and transaction limits. The money goes to mule accounts across several banks through IMPS and NEFT and is withdrawn quickly. Reports say about 20 banks, NBFCs and fintechs were affected; no loss figure has been made public.
Who Are CERT-In and CSIRT-Fin?
CERT-In (Indian Computer Emergency Response Team) is India’s national cybersecurity agency, working under the Ministry of Electronics and Information Technology (MeitY). Set up in 2004 and empowered under Section 70B of the IT Act, 2000, it responds to cyber incidents, issues security warnings and advisories, and coordinates cyber defence across government and industry. Organisations in India must report certain cyber incidents to CERT-In within six hours.
CSIRT-Fin (Computer Security Incident Response Team – Finance Sector) is CERT-In’s specialised unit for the financial sector. It works with banks, NBFCs, insurers, fintechs and payment companies to prevent, detect and respond to cyberattacks on India’s financial system.
What the CERT-In Advisory Says
According to MediaNama’s report on the CERT-In advisory, the attacks follow a clear pattern:
- Break in: attackers compromise internet-facing applications, exposed or outdated APIs, and admin systems that lack multi-factor authentication.
- Steal the keys: they collect payment gateway credentials and partner-bank API credentials, which are sometimes left in plain text in code or configuration files.
- Send money from inside: they call the company’s fund-transfer APIs from its own whitelisted servers, so the bank sees the requests as genuine. This skips the KYC, beneficiary and limit checks that normally sit in the app.
- Move it fast: transfers carry fake reference numbers, sometimes exceed normal limits, and go to mule accounts at multiple banks, where the money is withdrawn almost immediately.
- Cover their tracks: attackers delete or trim logs and tamper with security software.
The CERT-In advisory also notes that the time between a break-in and the first fraudulent transfer is shrinking, and that attackers may be using AI-assisted tools.
How Many Firms Were Hit?
The CERT-In advisory doesn’t name any company or give a number. However, media reports, summarised by The420.in, say about 20 banks, NBFCs and fintech firms were targeted earlier in October. Those reports link several attacks to weaknesses in a third-party payment and disbursement platform used by multiple lenders, including weak authentication and poor monitoring of payout APIs. The total amount lost has not been disclosed.
Why “No OTP” Makes This Different
Most frauds Indian users hear about involve tricking a person: a fake KYC call, a phishing link or a request to share an OTP. This attack is different. No customer is tricked at all. The criminals attack the company’s systems directly and pose as the company itself when talking to the bank.
That’s why the CERT-In advisory matters: it shows that even if customers do everything right, weak security at a fintech or its software vendor can still let money leak out.
What CERT-In Asked Companies to Do
The CERT-In advisory asks financial companies to tighten security around anything that can move money. Key recommendations include:
- Multi-factor authentication on payment platforms, admin portals, bank APIs and remote access
- Replace long-lived API keys with short-lived, per-session credentials, and store them securely, not in code
- Rotate exposed credentials and switch off unused or outdated APIs
- Maker-checker approval, where a second person must approve fund transfers
- Reconcile every payout against an approved loan or payment record
- Real-time monitoring for unusual transfer amounts, speed and new beneficiaries
- Report incidents to CERT-In and CSIRT-Fin
Should Customers Worry About the CERT-In Advisory?
For most people, the direct risk from the attacks in this CERT-In advisory is low. In these attacks, money is usually taken from the company’s own disbursement or settlement accounts, not from customers’ bank accounts. But there are three practical reasons to stay alert:
- Your loan records: if a fintech’s systems are compromised, fake loans or wrong disbursements could appear in its records. Check your loan app statements and your credit report for anything you don’t recognise.
- Follow-up scams: news of breaches often triggers fake calls and messages pretending to be “from your lender’s security team”. Never share OTPs, PINs or screen access with anyone who calls you.
- Where you borrow: use lenders that are registered with the RBI or partnered with RBI-regulated banks or NBFCs. Smaller, unregulated apps are more likely to cut corners on security.
If you spot fraud, call the national cybercrime helpline 1930 or report it on the National Cyber Crime Reporting Portal (cybercrime.gov.in), and inform your bank immediately.
The Bigger Picture: APIs Are the New Front Door
India’s digital lending and payment boom runs on APIs, which is exactly what this CERT-In advisory is about: the connections that let apps, fintechs and banks talk to each other in milliseconds. That speed is what makes instant loans and payments possible. But this CERT-In advisory shows the other side: every API key is a key to the vault. If it’s stolen, attackers can move money as fast as the system was designed to.
The lesson of the CERT-In advisory for the industry is that security has to sit where the money moves, at the API and payment layer, not only in the app customers see. On the other side, banks are now using AI to catch suspicious transfers in real time, as explained in our article on AI Fraud Detection in Banks.
Also read: UPI Merchant Fee Delayed
Also read: Spot and Report UPI Scams
Frequently Asked Questions
What is the latest CERT-In advisory about?
Advisory CIAD-2026-0046, issued on October 9, 2026, warns NBFCs, digital lenders, fintechs, payment companies and wallet operators that attackers are stealing payment and bank API credentials to make unauthorised fund transfers.
How many financial institutions were affected?
The CERT-In advisory doesn’t say. Media reports suggest about 20 banks, NBFCs and fintech firms were targeted in October 2026.
Did customers lose money?
No loss figures have been published. These attacks mainly target companies’ own disbursement and settlement accounts rather than individual customer accounts.
How did hackers bypass KYC and limits?
According to the CERT-In advisory, by using stolen API credentials to send transfer requests directly from the company’s trusted servers, which skips the checks built into the app.
What should I do if I notice suspicious activity?
Contact your bank or lender immediately, call the 1930 cybercrime helpline, and file a complaint on the National Cyber Crime Reporting Portal.
Conclusion
The latest CERT-In advisory is a wake-up call for India’s fintech and digital lending sector. Attackers are no longer just tricking customers; they’re stealing API keys and moving money directly from inside companies’ systems, bypassing KYC and limits, with no OTP needed. About 20 institutions were reportedly hit. For customers, the immediate risk described in the CERT-In advisory is limited, but it pays to watch your loan statements, ignore “security team” calls and borrow only from regulated lenders. For the industry, the message is clear: secure every API that can move money.
My take: In my view, this warning from CERT-In highlights a critical vulnerability that financial institutions must take very seriously. Securing the APIs and credentials that control direct financial transactions should be the highest priority. From a cybersecurity perspective, protecting only the customer-facing app is no longer enough. Every payment API should be secured with short-lived credentials, strong transaction-level authorisation, appropriate transfer limits and real-time monitoring. I would also prioritise independent reconciliation and maker-checker approval for high-risk transactions. Real-time monitoring helps spot suspicious activity early, but it must be backed by controls that can actually block unauthorised transfers.
As for fintech apps, I believe they earn trust only when they demonstrate strong security, regulatory compliance and accountability. Trust in digital finance should never be based on convenience alone; it must be earned by keeping funds secure at every stage of a transaction. I would conclude by saying: “When money moves at the speed of an API, security must work at the same speed, or even faster.”
Over to You
Do you trust fintech and instant-loan apps with your data and money, or do you prefer traditional banks? Share your thoughts in the comments below.